کانال تلگرام
پشتیبانی تلگرام
شماره تماس پشتیبانی:
0930 395 3766
ورود
ثبت نام
دنیاد
صفحه اصلی
گروه بندی
عکاسی
( Photography )
بازاریابی
( Marketing )
فیلم
( Video )
CAD
( CAD )
کسب و کار
( Business )
3D + انیمیشن
( 3D + Animation )
صدا + موسیقی
( Audio + Music )
طرح
( Design )
آموزش + Elearning
( Education + Elearning )
سلامتی و تناسب اندام
( Health & Fitness )
سبک زندگی
( Lifestyle )
توسعه
( Development )
تدریس و دانشگاهیان
( Teaching & Academics )
حسابداری مالی
( Finance & Accounting )
IT (فناوری اطلاعات ) و نرم افزار
( IT & Software )
شرکت ها
Linkedin (لینکدین)
Udemy (یودمی)
Pluralsight (پلورال سایت)
Skillshare (اسکیل شیر)
CBTNuggets
Packtpub
AloMoves
CloudAcademy
Coursera (کورسرا)
MasterClass (مسترکلاس)
خرید اشتراک
سفارش دوره یودمی
راهنمای سایت
جستجو:
انتخاب مرجع:
-- همه --
Linkedin (لینکدین)
Udemy (یودمی)
Pluralsight (پلورال سایت)
Skillshare (اسکیل شیر)
CBTNuggets
Packtpub
AloMoves
CloudAcademy
Coursera (کورسرا)
MasterClass (مسترکلاس)
مرتب سازی بر اساس:
مرتبط ترین
جدیدترین مرجع
پربازدیدترین مرجع
محبوبترین مرجع
جدیدترین دنیاد
مدت زمان دوره
جستجو کن
تعداد یافت شده:
170
مورد
آموزش Splunk 9: ایجاد اقدامات گردش کار
Splunk 9: Creating Workflow Actions
Joe Abraham
زمان دوره: 1h 4m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
شرکت:
Pluralsight (پلورال سایت)
آموزش SIEM: مدیریت رویداد با امنیت Splunk
SIEM: Event Management with Splunk Security
Nato Riley
زمان دوره: 0h 52m
انتشار مرجع:
آخرین آپدیت
بازدید مرجع:
1,986
شرکت:
Linkedin (لینکدین)
Master Splunk Enterprise Administration: Certification Prep
Master Splunk Enterprise Administration: Certification Prep
Usama Niazi
زمان دوره: 2 hours
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
161
شرکت:
Udemy (یودمی)
new
آموزش پیکربندی و مدیریت Splunk Indexer Cluster ها
Configuring and Administering Splunk Indexer Clusters
Johan Raeymaeckers
زمان دوره: 2h 6m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
-
شرکت:
Pluralsight (پلورال سایت)
آموزش ساخت گزارش ، داشبورد و هشدارها در Splunk
Building Reports, Dashboards, and Alerts in Splunk
Thomas Henson
زمان دوره: 1h 33m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
31
شرکت:
Pluralsight (پلورال سایت)
آموزش جستجوی پیشرفته و گزارش با Splunk Enterprise
Advanced Searching and Reporting with Splunk Enterprise
Muhammad Awan
زمان دوره: 3h 32m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
-
شرکت:
Pluralsight (پلورال سایت)
آموزش Splunk 9: مرتبط کردن رویدادها با تراکنش ها
Splunk 9: Correlating Events with Transactions
Karun Subramanian
زمان دوره: 1h 37m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
شرکت:
Pluralsight (پلورال سایت)
آموزش ساده کردن فرآیند واکنش به حادثه با Splunk
Streamlining Your Incident Response Process with Splunk
Aaron Rosenmund
Ryan Chapman
زمان دوره: 1h 13m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
42
شرکت:
Pluralsight (پلورال سایت)
آموزش 600+ Splunk سوالات مصاحبه تمرین تست
600+ Splunk Interview Questions Practice Test
Interview Questions Tests
زمان دوره:
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
992
شرکت:
Udemy (یودمی)
آموزش شکار تهدیدات سایبری SOC با Splunk
دانلود SOC Cybersecurity Threat Hunting with Splunk
Mohammad Mirasadollahi
زمان دوره: 2.5 hours
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
1,136
شرکت:
Udemy (یودمی)
آموزش آشنایی با Splunk: راهنمای عملی مدیریت
Getting to Know Splunk: The Hands-On Administration Guide
Tom Kopchak
زمان دوره: 4 hours
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
4,863
شرکت:
Udemy (یودمی)
آموزش Splunk 9: Building Reports, Dashboards, and Alerts
Splunk 9: Building Reports, Dashboards, and Alerts
Joe Abraham
زمان دوره: 1h 13m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
شرکت:
Pluralsight (پلورال سایت)
آموزش مدیریت Splunk Enterprise Security Data و داشبورد
Managing Splunk Enterprise Security Data and Dashboards
Joe Abraham
زمان دوره: 2h 20m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
-
شرکت:
Pluralsight (پلورال سایت)
آموزش Splunk Enterprise Administration: پیکربندی جستجوی توزیع شده
Splunk Enterprise Administration: Configuring Distributed Search
Karun Subramanian
زمان دوره: 1h 31m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
-
شرکت:
Pluralsight (پلورال سایت)
آموزش استفاده از مدل اطلاعات مشترک Splunk (CIM)
Employing the Splunk Common Information Model (CIM)
Adam Frisbee
زمان دوره: 0h 47m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
-
شرکت:
Pluralsight (پلورال سایت)
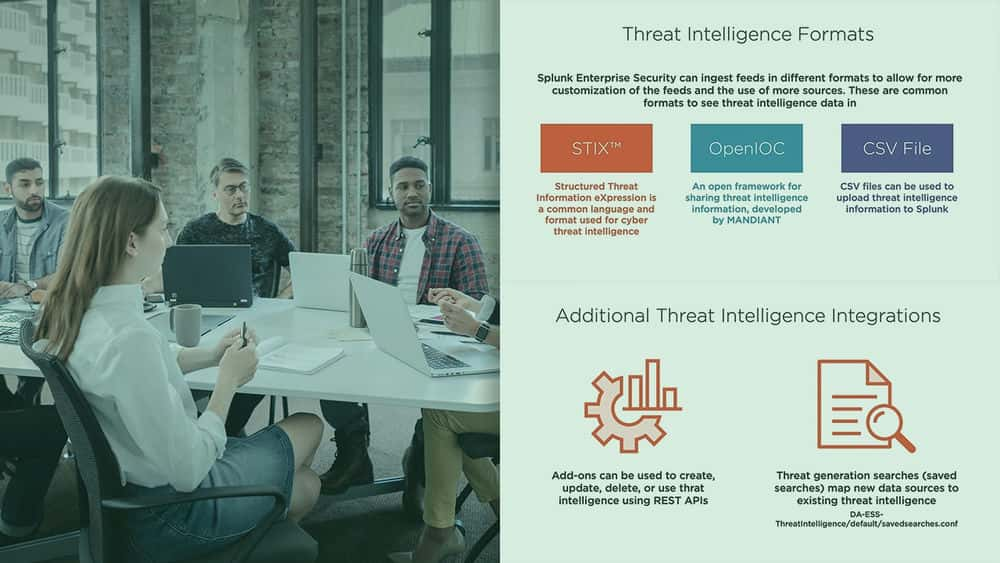
آموزش پیکربندی هوش تهدید در Splunk Enterprise Security
Configuring Threat Intelligence in Splunk Enterprise Security
Joe Abraham
زمان دوره: 1h 44m
انتشار مرجع:
آخرین آپدیت
ثبت نام مرجع:
-
شرکت:
Pluralsight (پلورال سایت)
1
.......
3
4
5
6
7
8
9
.......
11

 Joe Abraham

 Nato Riley

 Usama Niazi

 Johan Raeymaeckers

 Thomas Henson

 Muhammad Awan

 Karun Subramanian

 Aaron Rosenmund
 Ryan Chapman

 Interview Questions Tests
 Mohammad Mirasadollahi

 Tom Kopchak


 Adam Frisbee